French blood storage hit by freezer hacks as theories swirl
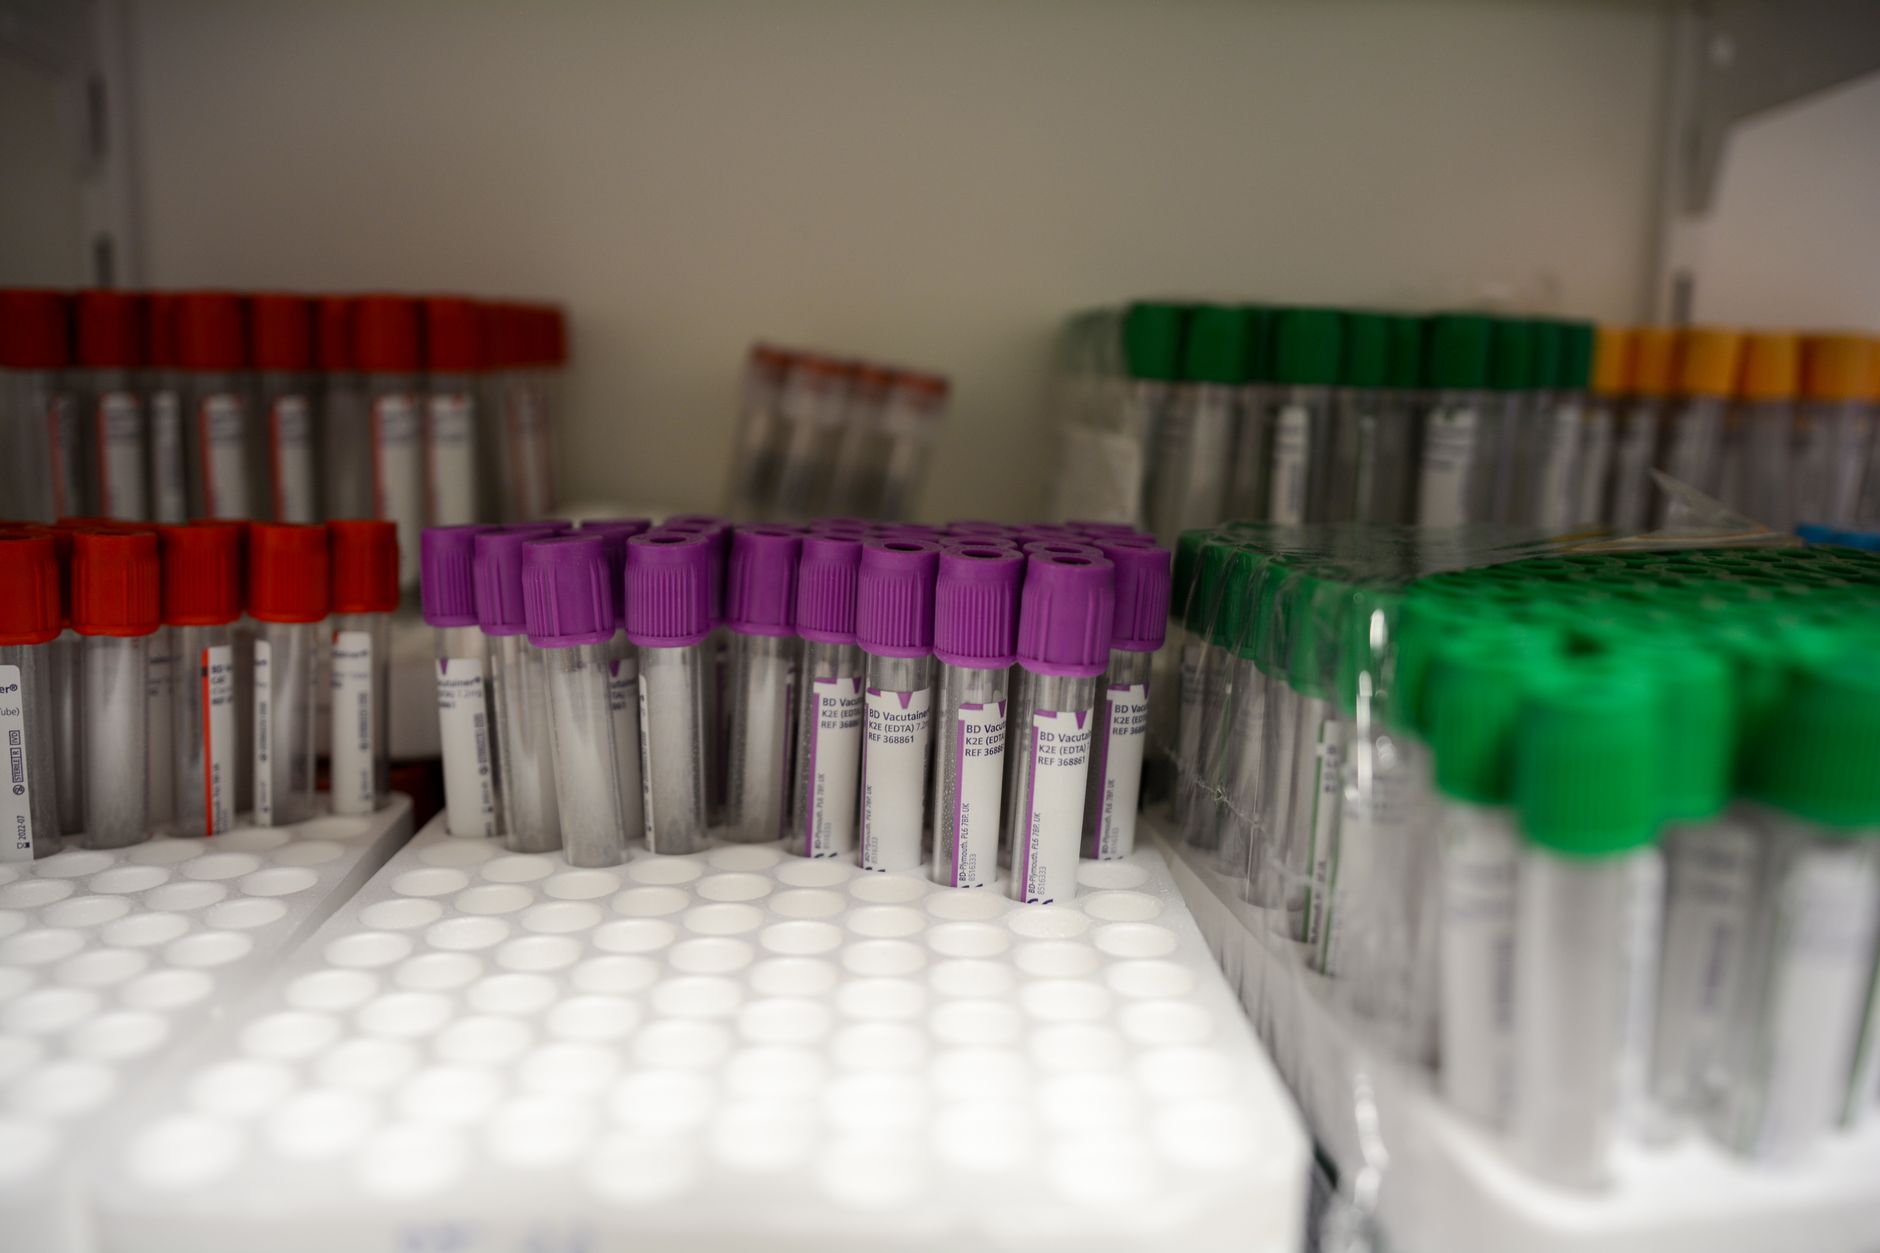
French authorities have confirmed that fridges storing donated blood in medical facilities were impacted by recent cyber-attacks carried out by unknown hackers. The French Blood Establishment (EFS) said that cold rooms storing blood were affected, with hackers setting temperatures to rise. Staff intervened to protect blood supplies, and the EFS stated: “No health impact has been identified and no loss of blood products is to be reported.”
Until now, only supermarkets were known to have been impacted by these hacks. Online rumours suggest Russian hacktivist groups claimed a joint hack of one system used in attacks affecting European supermarkets. Groups named Noname057(16) and Z-Pentest Alliance posted that they successfully hacked Danfoss, leading to speculation they were behind the freezer hacks. But analysts question whether that meant they were behind the supermarket cyber-attacks.
Honeypots reveal coordinated targeting
Cyber-security researchers at multiple firms are examining evidence from “honeypots” for clues. Three separate cyber-security firms deployed fake freezer software traps to monitor hacker attempts. A honeypot is a digital decoy—a fake computer network or file set up to look vulnerable, luring and trapping hackers. The second wave hitting several European countries was highly targeted, according to activity gathered after the first wave.
Ryan Dewhurst of the Spanish cyber-security company Previdian said: “The fact that all these fridge freezers were hit simultaneously suggests planning and coordination.” The entry point to affected freezer software products was not difficult to exploit, being poorly protected, with known attack methods already available online. Dewhurst noted that hackers had to gather devices’ public IP addresses to create a target list, plan methods and timing. He added: “Given the reported timing of when the devices had their temperatures increased, which seems to have been overnight for maximum damage – this is further evidence that the attack was planned and co-ordinated.”
Possible culprits and prior incidents
Lupovis, a Strathclyde-based cyber firm, deployed similar honeypot technology. Their honeypots appeared located around the world, with activity starting 10 days before the second wave. The Lupovis team saw hackers scanning and probing fake freezer sites only in Europe. Dr Xavier Bellekens, Lupovis founder, said: “We saw none of our honeypots in places like Africa or South America targeted at all.” Sekoia, a French cyber-defence firm, also noticed scanning activity prior to the second wave but said it could have been automatic scanning without malicious intent.
Sekoia’s report to customers suggested the attack nature aligned with Russian hacktivists or the Russian government, accused of “hybrid warfare” cyber-attacks across Europe. Their research also pointed to Iranian regime hackers or hacktivists. The report noted: “Iranian-aligned actors have an established record of targeting internet-exposed industrial control systems and previous incidents involved the same equipment in Israel and the US – both adversaries of Iran.” Sekoia said about 40 Israeli supermarkets running Danfoss controllers were compromised in 2022. In late August, freezers at at least six US military bases were forced into defrost mode, as in France, though controller models were unconfirmed and investigations ongoing.
Ongoing investigations and future threats
A Sekoia spokesperson told the BBC: “To date, we have no technical evidence indicating the involvement of Russian-speaking groups.” The spokesperson added: “Furthermore, as NoName057 is not known to effectively conduct operations beyond DDoS attacks and has a history of making false attributions, we remain sceptical of their alleged claim of responsibility.” DDoS attacks involve flooding a website or online service with internet traffic to throw it offline or make it inaccessible.
Authorities in several countries are actively investigating the hacks and warning supermarkets about potential future attacks. None of the three cyber firms gathering honeypot data is ruling out a teenager. Experts agree the degree of planning necessary means a well-coordinated group, and they would expect online bragging to surface soon. Sekoia said the possibility remains that all three waves were carried out by different, distinct groups or copycats. Shop freezers in seven European countries have been hit by the cyber-attack.